By William Weiner September 24, 2026
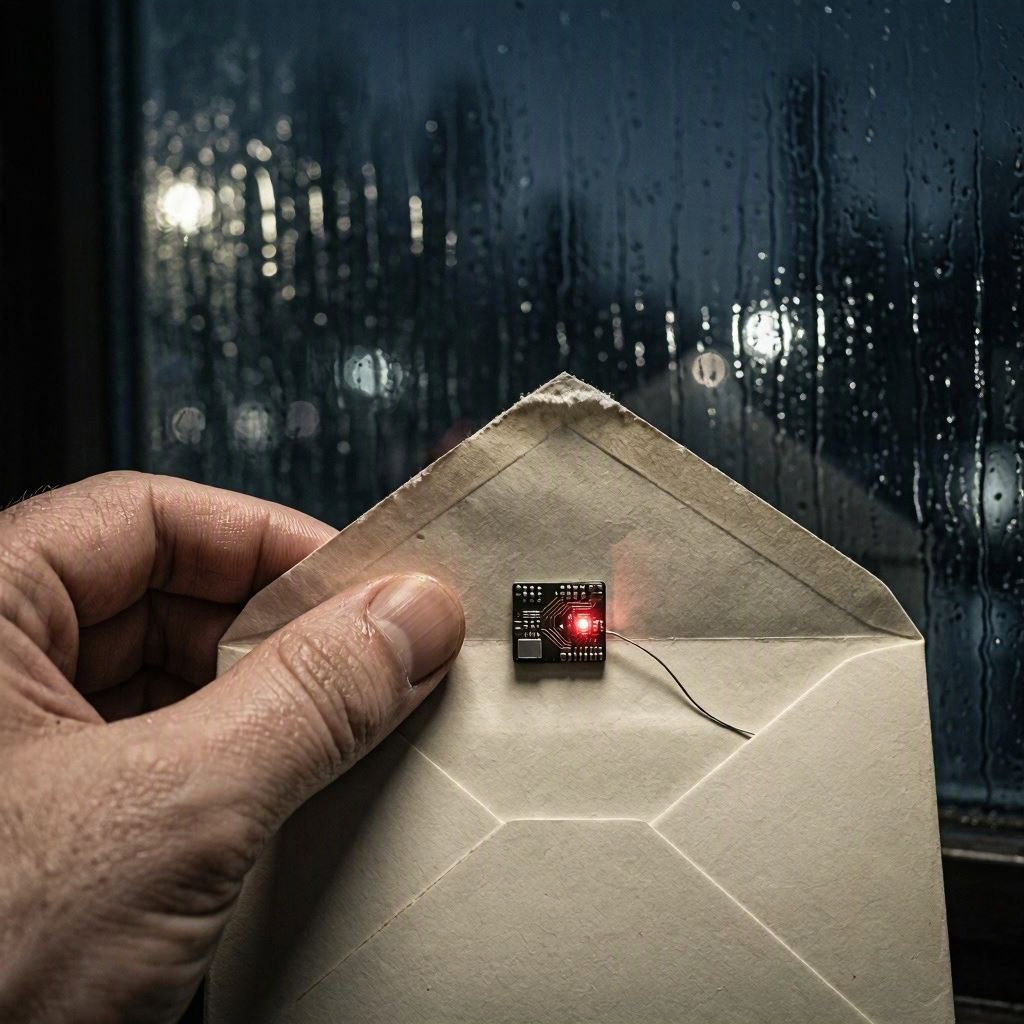
Imagine a letter arrives in your mailbox. Ordinary envelope, nothing remarkable about it. Except taped inside the flap is a small device: the moment you open the envelope, it reports back to the sender the exact time and your location. Not because you asked for that. Not because you agreed to it. Because they wanted to know, and the technology to find out was cheap enough to include.
We’d call that a crime. Tampering, surveillance, something. Nobody would accept “well, you opened the envelope” as a defense.
That exact thing happens in your email inbox every few minutes, and almost nobody blinks.
It starts with the envelope
The mechanism is a single-pixel image, invisible, embedded in the body of an email. Your mail client fetches it automatically the moment you open the message; this fetch alone reports the time and the IP address you’re connecting from, which by itself is enough to place your approximate location. It doesn’t stop there: the same request typically hands over your device type and OS version too, and often enough which mail client you’re using, lifted from content request headers your device sends without asking you. You didn’t click anything. You didn’t reply. You opened a message, the way you’ve opened mail your entire life, and that act alone was reported. And the pixel is only the simplest version of the trick: the same signal rides on any remote content a message loads when it’s opened, a background image, a linked font, a stylesheet, and most of the tools built to stop this only catch the pixel, not the pattern.
That’s the floor. It gets worse the more you engage, not because you did anything wrong, but because engaging with an email was never redesigned to be safe.
Click a link in a marketing email and you’re very likely not clicking the link you think you’re clicking. It’s a redirect through a tracking domain, unique to you, that logs the click, attributes it to your specific recipient ID, and then, only after logging it, forwards you to the actual page. The link in the email and the link your browser follows are two different things wearing the same blue text.
Reply to it, or forward it to someone else, and in a lot of commercial mail there’s a third layer sitting underneath the first two: identifying information quietly embedded in the message body itself, in HTML comments or meta tags nobody renders and nobody reads, that travels with the copy. It doesn’t reliably get back to the original sender the way a pixel or a link does. That’s not the point. The point is the email itself has been “watermarked”. Your reply, your forward, the thing you now think of as your own words, is carrying someone else’s fingerprint through the rest of its life. And the pixel and the tracked links inside it are still live too, so when you forward the message, they fire again for the next person. Forwarding doesn’t confuse the tracking, it extends it: the same identifiers that were tracking you now fire from your contact’s device too, and that’s enough for the sender to start connecting the two of you, without ever having to ask.
None of this is incidental. It’s the entire reason the other two exist. Marketers can roll opens and clicks into an engagement profile that influences future campaigns — for example, whether someone receives another message or is moved into a different segment. Separately, mailbox providers use their own signals to decide whether incoming mail belongs in the inbox or spam. The tracking isn’t a side effect of email marketing. It is the business model. The message is the delivery vehicle for the measurement.
The double standard nobody says out loud
If a stranger built a profile of your daily movements, purchases, habits, and associations without your meaningful consent and sold access to that profile to other companies, we have a word for that, and the word is not “marketing.” We prosecute people for stalking with a lot less data than a mid-size advertiser has on the average inbox.
But do the identical thing through a checkbox buried in a signup flow, route the data through a company with an office and a privacy policy, and it stops being a violation and starts being Tuesday. Identity theft is a crime because someone got your information without your consent and used it against your interest. Rebuilding the same profile, one open and one click at a time, and selling access to it, is a business plan, as long as you did the paperwork. None of this means every identifier hidden in an email breaks a law. It means there’s a basic difference between information the recipient can see and information secretly attached to their copy of the message for the sender’s benefit.
Nobody sat down and decided this was the right line to draw. It’s just where the money landed.
How we got here
Email wasn’t designed as a behavioral measurement platform. It started as a protocol between people, no different in spirit from a letter: you wrote something, it went to the person you sent it to, and that was the whole transaction. What changed wasn’t the protocol. It was the business model wrapped around it. Once “free” email and “free” marketing tools needed to be paid for by something, they were paid for by attention, measured in opens and clicks, and email quietly stopped being a message and started being an instrument.
Nobody voted on that. There was no announcement, no terms-of-service update you could have objected to, because the tracking didn’t arrive as a feature you opted into. It arrived as infrastructure, baked into the tools every marketing platform ships by default, invisible unless you go looking for it. By the time it was ubiquitous, it was also normal, and normal is a hard thing to argue with, because it no longer feels like a decision anyone made.
The law is catching up, but only halfway
Here’s the thing worth sitting with: you don’t have to squint to see this as wiretapping, because in a growing number of states, that’s exactly the argument being made in court, right now, under laws that predate the internet by decades. California’s Penal Code Section 631, an all-party-consent wiretapping statute from 1967, is the basis for pixel-tracking lawsuits filed in the last couple of years. Florida has its own wave under its interception statute. Illinois, Pennsylvania, and New York all have active cases running the same theory: that quietly capturing a read event, a click, a piece of engagement, without real consent, is the same category of act the law has punished for fifty years when it happened over a phone line.
Courts haven’t adopted a single rule here, and the outcome depends heavily on the statute, the jurisdiction, and the facts of each case. But the instinct behind that letter-opening device at the start of this piece isn’t fringe outrage. It’s already sitting in front of judges as a straightforward legal claim, decided under statutes nobody wrote with email in mind, because the underlying act didn’t need a new law to be recognizable as a violation.
This isn’t only a US argument, and Europe hasn’t actually found the clean framing either, even with more regulatory machinery pointed at the problem. France’s CNIL and Italy’s Garante both moved in 2026 to require real opt-in consent before a personalized tracking pixel can log whether you opened an email, treating the pixel the same way cookie law already treats a tracking cookie: as access to your device that requires permission first. That sounds like the right instinct. Then look at what each rule carves out. France exempts pixels used purely for deliverability tracking, which is exactly the category feeding the engagement profile described above. Italy exempts anonymized aggregate pixels. Neither rule touches personalized tracking links or CSS-based loading, mechanisms doing the identical job by a different route. Regulators on both sides of the Atlantic have converged on the same narrow question: was there a checkbox. Nobody with the authority to write the rule has asked the question this piece is asking, whether logging a private act like opening a letter should require an exemption to be acceptable at all, rather than a justification to be forgiven.
Who is email for
That’s the actual question. Not “is this spam,” which is a permission test that legitimate advertisers pass without even trying. Not “is this legal,” which depends on which state you’re standing in. The question is simpler than either of those: when you open, click, reply to, or forward an email, who is that action actually serving? You, or the machinery riding along with it that was never mentioned to you and never asked for your permission in any way you’d recognize as consent?
For most email sent to most people today, honestly, the answer is both, and the second one is winning.
What to actually do about it
None of this fixes itself, and none of the following is a complete answer. But it’s a start, and it costs you almost nothing to begin.
Turn off automatic remote image loading. Many major mail clients and services let you block or restrict automatic loading of remote images, and almost nobody enables it. It’s the single most direct way to stop firing pixels on your own behalf, and it takes two minutes.
Use a client that shows you what’s actually happening. Thunderbird and a few others surface remote content and let you see, case by case, how much of what lands in your inbox is carrying tracking machinery. Seeing the volume for yourself does more to change your mind than any article, including this one.
Say it out loud. Tell the businesses and people you deal with that you care about this. Cite tracking, not volume, when you unsubscribe. Make privacy something you’re known to expect, not something you quietly enforce with a settings toggle nobody else sees.
Know that this fight isn’t hypothetical. It’s in courtrooms in California, Florida, Illinois, Pennsylvania, and New York right now, under existing law, and it’s the subject of active rulemaking in France and Italy. That’s worth paying attention to, and worth supporting when you get the chance, whether that’s a public comment period, a legislator, or an organization already doing the work. Just don’t mistake a consent checkbox for the argument actually being won.
Until the defaults change, control what you can. The settings and client changes above only reach remote-content tracking, and even then, some of them catch pixels specifically and miss the rest of the pattern. None of it touches the tracking baked into the content itself, or the profile being built about you in marketing databases somewhere you’ll never see. Those are the pieces email client settings can’t reach, and that’s the actual reason EMail Parrot exists: not just to filter threats out of your email, but to make sure nothing you receive, from anyone, carries an identifier back to a real you, and to give you practically unlimited variants of your address to hand out, each one still routing straight back to you.
Email used to be a way to talk to people. It can be again. It just requires deciding, out loud, that being watched isn’t the price of admission.
Questions about migrating? Email us at info@emparrot.com.